Just Educational Purpose Only For Pentesters And Developers

  • challenge

    I was addicted to hacking, more for the intellectual challenge, the curiosity, the seduction of adventure; not for stealing, or causing damage or writing computer viruses. Kevin Mitnick

    Read More
  • Computer hacking

    Computer hacking really results in financial losses and hassles. The objectives of terrorist groups are more serious. That is not to say that cyber groups can't access a telephone switch in Manhattan on a day like 9/11, shut it down, and therefore cause more casualties.Kevin Mitnick

    Read More
  • The only Entertainment

    Hacking was the only entertainment that would occupy my mind - like a huge video game, but with real consequences. I could have evaded the FBI a lot longer if I had been able to control my passion for hacking.Kevin Mitnick

    Read More
Showing posts with label SQL injection. Show all posts

Wednesday, May 13, 2015

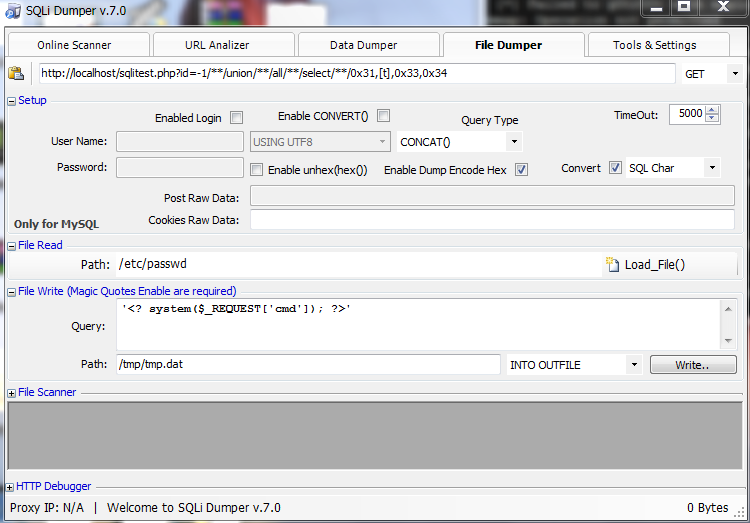
SQLi Dumper - Advanced SQL Injection\Scanner Tool v7.0 Private Version


Designed to be automated to find and exploit web security vulnerabilities in mass from worldwide!
It is robust, works in the background threads and is super faster.
Uses an advanced search engine with 10 different online search services.

Last release: 06/23/2014 v.7.0

SQLi Dumper Features:

-Suports 20 methods of SQL Injection;
-Suports Multi. Online search engine (to find the trajects);
-Automated search for data in a bulk URL list;
-Automated analizer and dumper with custom injections points (URL, POST, Cookies, UserLogin or UserPassword);
-Dumper suports dumping data with multi-threading (databases/tables/columns/fetching data);
-Exploiter, Analizer and Dumper suports up to 50x separeted threads;
-Advanced WAF bypass methods;
-Advanced custom query box;
-Dumper can dump large amounts of data, with greats control of delay each request;
-Easy switch vulnerabilities to vulnerabilities (internal database);
-Suports proxies list;
-GeoIP database;
-Advanced Trash System works with millions of urls;
-Admin login finder;
-Standalone .exe (no install).
credit -> http://sqldumper.blogspot.com


Download
click to begin
2.2MB .zip

Thursday, May 7, 2015

SQL Injection Bypassing HandBook


Content writers :-

Chapter I:::


  • SQL Injection: What is it?
  • SQL Injection: An In-depth Explanation
  • Why is it possible to pass SQL queries directly to a database that is hidden behind a firewall and any other security mechanism?
  • Is my database at risk to SQL Injection?
  • What is the impact of SQL Injection?
  • Example of a SQLInjection Attack

WebApplication Firewalls::

  • Detecting A WAF
  • Prompt Message
  • Dotdefender
  • Observing HTTP Response

Chapter II

Advanced evasion techniques for defeating SQL injection Input validation mechanisms
Web applications are becoming more and more technically complex. Web applications, their

  • Whitespace
  • Null Bytes
  • SQL Comments
  • URL Encoding
  • Changing Cases
  • Encode to Hex Forbidden
  • Replacing keywords technique
  • WAF Bypassing – using characters
  • HTTP Parameter Pollution (HPP)
  • CRLF WAF Bypass technique
  • Buffer Overflow bypassing

Chapter III

Let's see the matter in an orderly fashion from the beginning

  • See If Site vulnerability Or Not
  • Get Column Number
  • Bypassing union select
  • Get Version
  • Group & Concat
  • Bypass with Information_schema.tables
  • Requested Baypassing

Chapter IIII

Other issues related to the subject
  • Null Parameter
  • FIND VULNERABLE COLUMNS
  • Count(*)
  • unhex()
  • Get database
  •  
Download : MediaFire